About North Avenue
Our Managing Principal
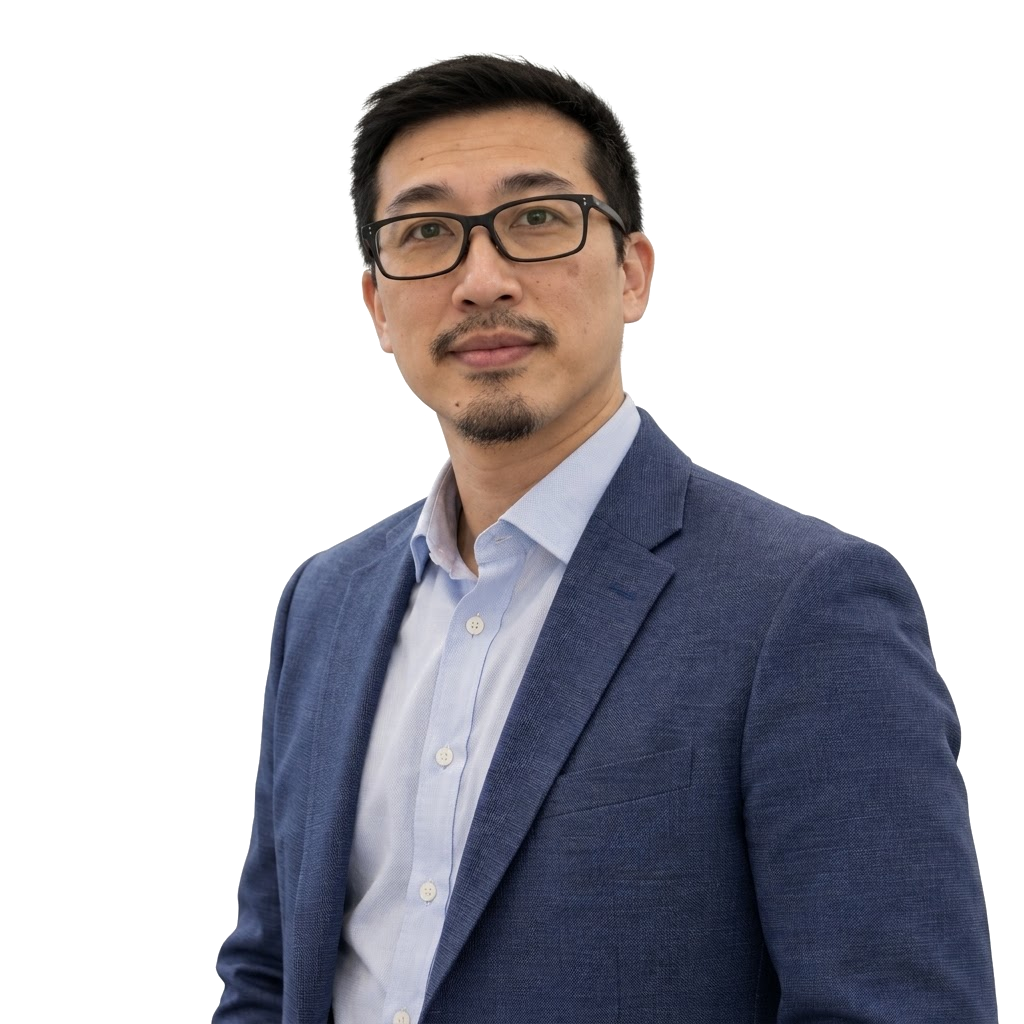
Kevin Hsiao is the founder and Managing Principal of North Avenue. He has spent more than 30 years in enterprise technology, the last decade building and leading cybersecurity, risk, and compliance programs for global, regulated, and private equity-backed organizations, and has sat on both sides of the audit table: first as a consultant and PCI Qualified Security Assessor at Protiviti, where he led compliance audit engagements and architected the PCI DSS remediation plan for non-compliant clients; later as the one answering to auditors himself at Sage, First Advantage, and Perseus Group.
Kevin holds an MBA from Emory University's Goizueta Business School, a Bachelor's degree in Electrical Engineering from Georgia Tech, and is a Certified Information Systems Security Professional (CISSP). He founded North Avenue on a simple premise: cybersecurity should be measured by how much more confidently a business can execute, not by how many boxes it checks.
Most recently, Kevin built the enterprise Information Security Program at Perseus Group from the ground up, standing up SOC, security engineering, and GRC functions for a decentralized portfolio of more than 85 businesses, and led the company's GenAI governance and the security controls that enabled Microsoft Copilot's rollout to more than 1,000 users. At First Advantage, a background-screening company that went from privately held to private equity-backed to publicly traded on NASDAQ during his tenure, he served as Deputy CISO and then as Information Security Program Head, taking on responsibility for enterprise cyber risk following the CISO's departure.
Our cyber risk philosophy
The security metrics most executives and boards see measure the wrong thing: vulnerabilities closed, phishing click rates, MFA coverage. Those numbers matter, but they don't tell a CEO whether security is creating business value. Can the business enter a new market? Acquire a company? Deploy AI? Move workloads to the cloud?
What a cyber risk program should look like depends on the business carrying it. Its risk tolerance, its industry, its regulatory exposure, and what it can realistically sustain day to day. A framework is the starting line, not the goal.
It's not possible to eliminate risk entirely, every business carries some. North Avenue helps leaders and boards understand the risks they're actually holding, bring forward clear recommendations grounded in the business's own context, and let the business decide how it wants to move forward. The judgment call belongs to leadership, not to an outside advisor.
"How much more confidently can an organization execute because of its security program? That's the difference between security as an insurance policy and security as an enterprise capability."
Our position on AI security
AI security is the same discipline, moving at a faster pace, and it is the risk topic most organizations struggle with. North Avenue treats AI security as a core pillar of its services, focusing on what matters most: the data.
- What data is AI allowed to access?
- What is it allowed to do with it?
- How is its output validated?
- Who is accountable for its actions?
"Most AI already inside a business didn't arrive through a strategic initiative. It arrived through the loan origination system, the CRM, the HR platform, turned on by default. That's shadow AI."
Two patterns matter most in practice. AI agents need the same lifecycle management, least-privilege access, and logging any service account with the power to move money would require: that's the non-human identity conversation, already playing out across nearly every environment whether or not it's been named that way yet. The second is shadow AI: it shows up across dozens of vendors, cloud and desktop software alike, often turned on by default with little notice and a painful, multi-step opt-out process, already inside the perimeter before anyone runs a risk assessment.
None of this requires reinventing governance from scratch. Model risk management, the discipline banks already use under SR 11-7 and OCC 2011-12 to validate and monitor models, isn't obsolete, just calibrated to the wrong pace and scope for what's coming; the cadence needs to adapt, not the structure. And the old engineering adage still applies: garbage in, garbage out. The cleaner the underlying data, the better the model's grounding, and the more defensible the outputs a business can act on.
Our key engagement principles
These are the operating principles behind how North Avenue approaches every engagement.
Security is understanding the business
For a cybersecurity program to succeed, understanding what matters to the business comes first. What does success look like? How much risk is acceptable? What are the crown jewels, and where are they stored? That understanding is the foundation a lasting security program is built on.
Security risk is business risk
A cyber incident shows up on the balance sheet, in customer trust, and in board minutes, not just in an incident log. Security decisions get evaluated with the same rigor as any other risk the business carries. Understanding that impact on the bottom line keeps everyone aligned.
Security is culture, not compliance
A passed audit doesn't mean an organization is secure. Frameworks like NIST and ISO offer useful reference structure, but their controls only matter once they're tailored to fit the business's actual risk appetite. Durable security is a culture of shared responsibility, not a checklist.
Start a conversation
Tell us a bit about your business, the issues you're trying to tackle, and where North Avenue might help.